 Ships It Friday
1 / 3
Signed in since March
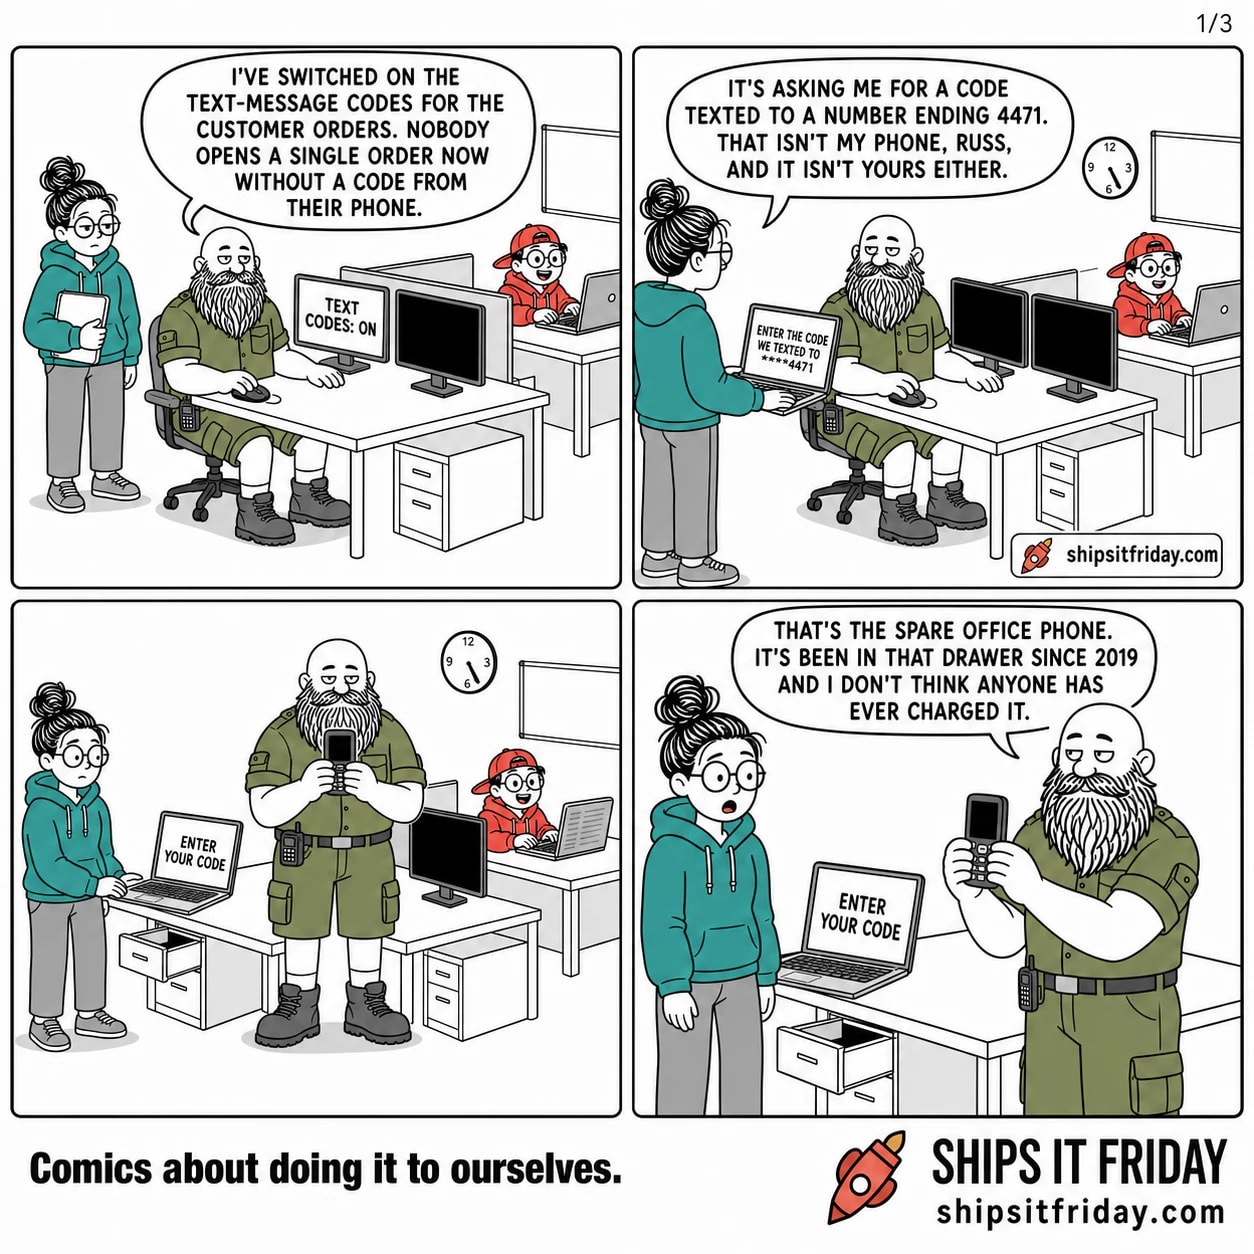
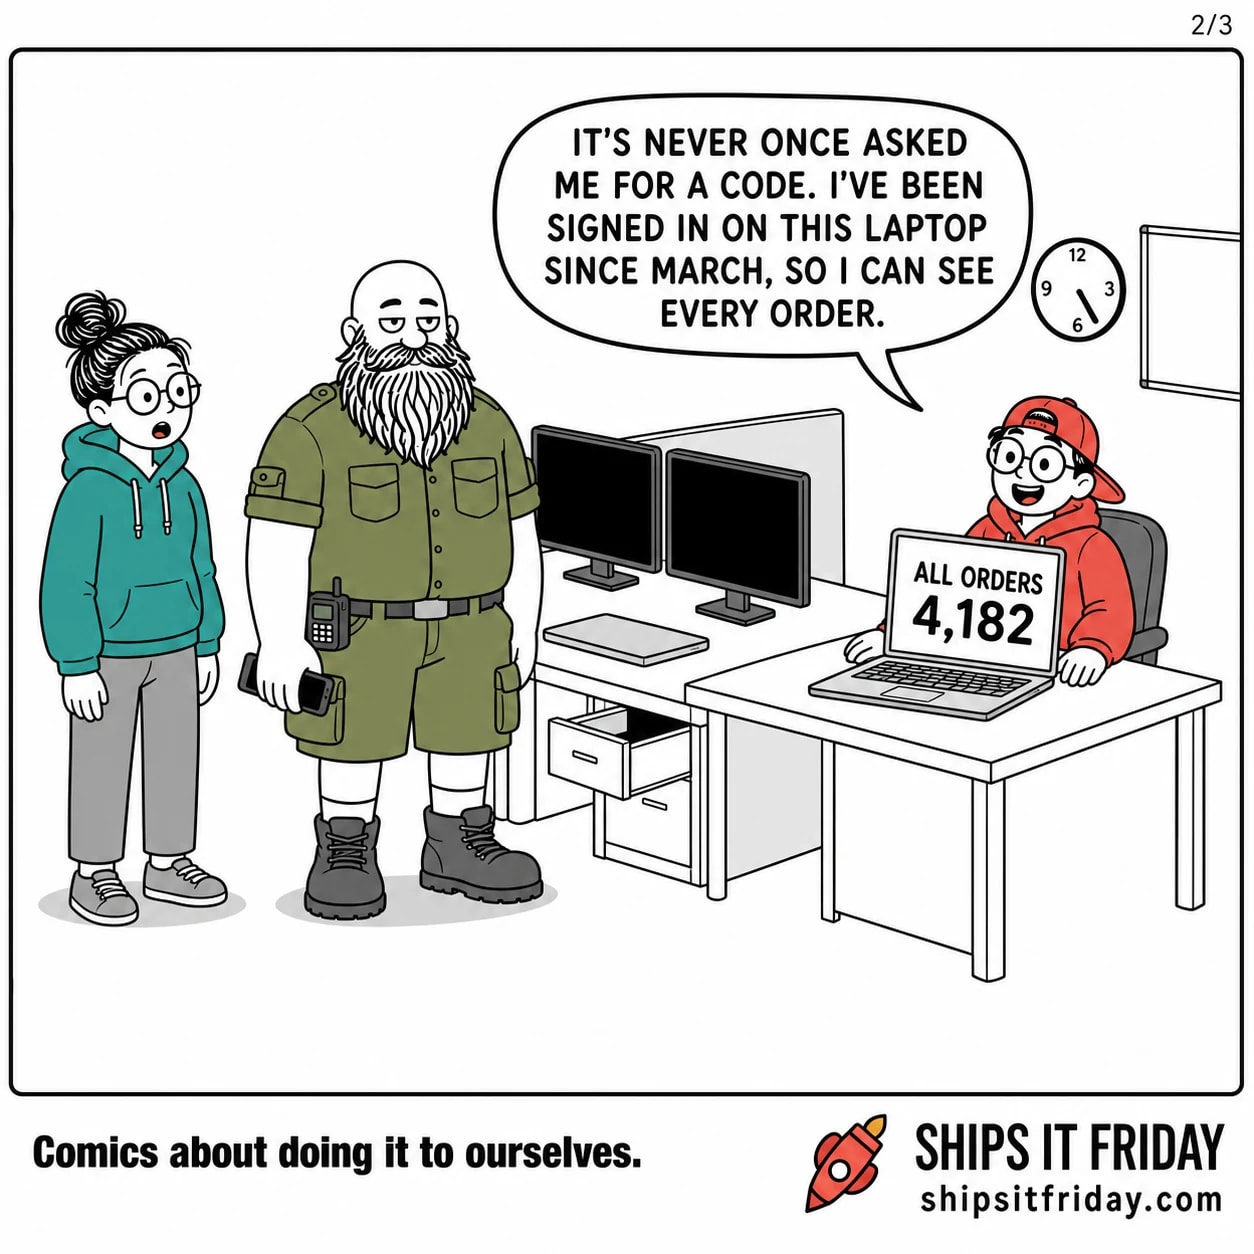
Russ put the customer orders behind a texted code so nobody could open one without it. The code went to a spare office phone dead in a drawer since 2019.
The mistake
The team turns on SMS-based one-time codes for accessing customer orders, but the number configured to receive those codes belongs to a spare device that has sat powered off in a drawer since 2019, so nobody can complete authentication. Meanwhile, a session opened on the intern's laptop months earlier was never invalidated when the new code requirement went live, so it bypasses the check entirely and stays fully authenticated. Turning on a new auth requirement doesn't revoke pre-existing sessions, and nobody confirmed the SMS destination was even a live, reachable number before switching it on.
- security
- logins
- admin-tools
- ops
- customer-support